Give access an expiry date, not a permanent place in your business
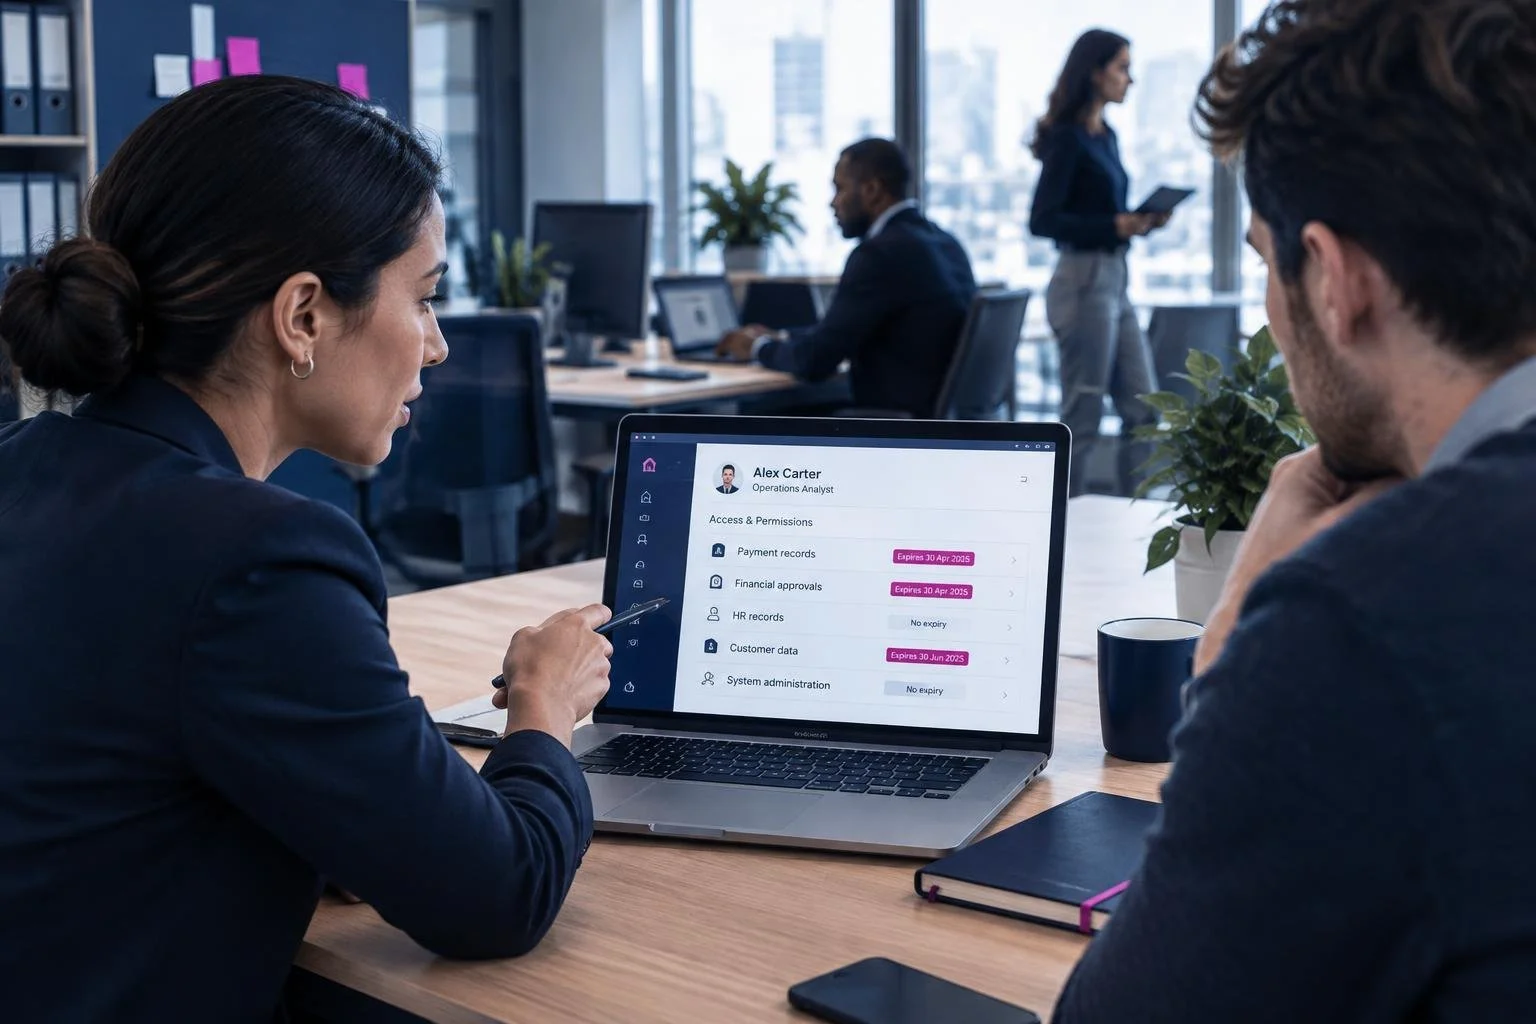
Someone moves from finance into operations. Their new permissions arrive promptly, but their old access to payment records stays put. Nobody complains, nothing breaks, and the move is considered complete.
That’s how an access problem can grow without anyone making an obviously bad decision. Businesses are good at helping people get started. They’re often less organised about removing permissions when responsibilities change.
For business leaders and internal IT teams, the challenge isn’t simply to tighten security. It’s to make sure access changes with the work, without making everyday tasks unnecessarily difficult. Our recommendation is straightforward: every permission needs a current purpose, and temporary access needs a planned ending.
The risk is bigger than administrator accounts
Administrator rights deserve attention because they can allow someone to change systems, manage users or disable protections. But excessive access isn’t limited to technical privileges. Being able to download employee records, view commercial negotiations or amend supplier details can matter just as much to the business.
Permissions accumulate through perfectly ordinary events. Someone covers a colleague’s duties, joins a project or helps with a system migration. A supplier gets access for troubleshooting. The immediate need is understood, but the ending is left vague.
Over time, an account can carry a history of someone’s employment rather than a sensible description of their current job. This is often called privilege creep. It’s particularly easy to miss when the person still works for the organisation, because their account looks legitimate and remains in daily use.
That doesn’t make the employee untrustworthy. It makes the consequences of a mistake or compromise harder to contain. If an attacker steals their credentials, the permissions attached to the account help determine what the attacker can reach. Stronger sign-in protections and threat detection still matter, but they don’t remove the need to limit access behind the sign-in screen.
The useful distinction is between preventing an intrusion and containing its impact. A business needs both.
Start with the permissions that could hurt most
A company-wide review can feel overwhelming, especially when access is spread across cloud applications, shared folders and older systems. Trying to inspect everything at once can produce a large spreadsheet that nobody has time to resolve.
Start instead with the systems where unnecessary access could cause the greatest harm. That might mean payroll, financial approvals, sensitive customer information or the accounts used to administer your technology.
For each, identify who can get in, what they can do and who can decide whether that access is justified. Include external suppliers, shared accounts and permissions inherited through group membership. A list of named users alone may miss important routes into the system.
Then ask owners to assess access against actual work. Could this person explain which current responsibility requires this permission? Is viewing enough, or do they need to edit? Do they need access to the whole dataset or a smaller part?
Avoid treating recent activity as the sole test. Some legitimate duties happen infrequently. Equally, someone using a permission doesn’t prove they should have it. Usage is evidence to consider, not a substitute for judgement.
Make removal part of the original request
It’s much easier to agree when access should end while everyone remembers why it’s needed.
A temporary request should name the task, the approving owner and an expiry date or review point. If someone needs extended access, that should trigger a fresh decision rather than silently turning a temporary arrangement into a permanent one.
Role-based permissions can make this easier. A defined set of access for a purchasing role, for example, reduces the temptation to copy everything from a long-serving colleague’s account. But roles also need maintenance. If the standard role becomes a collection of every exception anyone has requested, the same problem returns under a tidier label.
Not all access should expire automatically. Core permissions for an ongoing role may be better handled through reviews and change triggers. Elevated access for a short maintenance task is a stronger candidate for a fixed end time. The point is to choose a sensible lifecycle, not impose identical rules everywhere.
Build access checks into events the business already recognises: role changes, project closure, supplier contract endings and changes in system ownership. For a role move, reviewing the old permissions should be part of completing the move, not an optional clean-up afterwards.
Share the decisions, but be clear about ownership
IT can often show what access exists and carry out changes. It can’t reliably decide whether someone still needs a particular set of financial reports or access to a confidential business project.
That judgement belongs with the people responsible for the work and the information. Managers should confirm current responsibilities. System or data owners should approve the access those responsibilities require. IT should implement the decision and retain evidence of what changed.
Where an internal team and a managed service provider share delivery, agree who receives change notifications, who approves removal and who checks it happened. Otherwise, a request can be closed in one system while permissions remain active elsewhere.
This is where connecting everyday operations with improvement matters. Automating a reminder, routing an approval or applying a documented expiry can reduce repetitive administration. But automation needs a clear decision behind it. It won’t resolve an owner who no longer exists or an approval rule nobody understands.
Remove access carefully, not timidly
There’s a real trade-off here. Removing permissions without understanding dependencies can interrupt legitimate work. Leaving everything untouched because something might break makes unnecessary access the default.
For uncertain or sensitive changes, confirm the dependency with the owner, agree a suitable change window and prepare a controlled way to restore essential access if needed. Any restoration should have a reason and a review point, so the exception doesn’t quietly become permanent again.
Shared and emergency accounts need particular care. Establish ownership, understand their purpose and review how their use is recorded. Don’t disable an account blindly if a critical process may depend on it, but don’t accept uncertainty as a reason to leave it unmanaged indefinitely.
Leadership reporting should reflect this work. Alongside blocked threats and investigated alerts, track overdue access decisions, temporary permissions past their agreed end date and important systems without a named owner. These measures expose unfinished work, although they aren’t proof that every remaining permission is safe.
The goal isn’t the smallest possible permission list. It’s access the business can explain and justify today. People should have what they need to work, with a dependable process for taking it away when that need ends. That’s a practical security discipline, not an annual paperwork exercise.