You Have More Tech Than You Think, and That’s Okay, Start With Ownership, Not Inventory
Have you ever signed up for a tool to fix one problem, only to find you and three colleagues are still logging into five different systems to complete the same task? If that sounds familiar, you are not alone. Growing businesses accumulate applications, integrations and supplier connections gradually, and before long the estate is harder to reason about than anyone expects. That ambiguity creates security gaps, frustrates employees, and makes sensible automation or AI risky.
This piece explains a practical way out. The goal is not to build the perfect inventory overnight, but to create an operating habit that keeps visibility current and ties decisions to business impact. I’ll explain what to look for, why ownership matters more than a spreadsheet, and how to make AI, automation and security safer choices as you scale.
Start with questions that matter to the business
Too many discovery exercises begin with lists of software and license counts. That is useful, but incomplete. Leaders should work from the outcomes they care about, then map technology back to those outcomes. Useful starter questions are:
Which services or datasets would cause the most operational or reputational damage if they failed or were leaked?
Which tasks force people to hop between multiple systems to do a single piece of work?
Where do support teams repeatedly see the same unresolved issues because nobody owns the system end to end?
These questions move the conversation from abstract asset counts to concrete business exposure. They also help prioritise where to focus limited time and budget, which is essential for growing organisations.
Make ownership the first control
Ownership does not mean a single person does every job. It means clear, recorded responsibility for three things: who can access a system, who is accountable for its data quality, and who decides whether the system stays, gets replaced or is retired.
When ownership is absent, systems silently drift. Integrations are left undocumented, forgotten accounts remain active, and permissions grow. Those gaps are where risk lives, because tools alone will not close them.
Practically, assign owners and give them a simple remit: maintain an operational summary. That summary need only cover what the system does, who uses it, what data it holds, what integrations exist, and which SLA or monitoring applies. Keep the summary short and easy to update, so it becomes part of normal work rather than a compliance chore.
Map tasks, not just applications
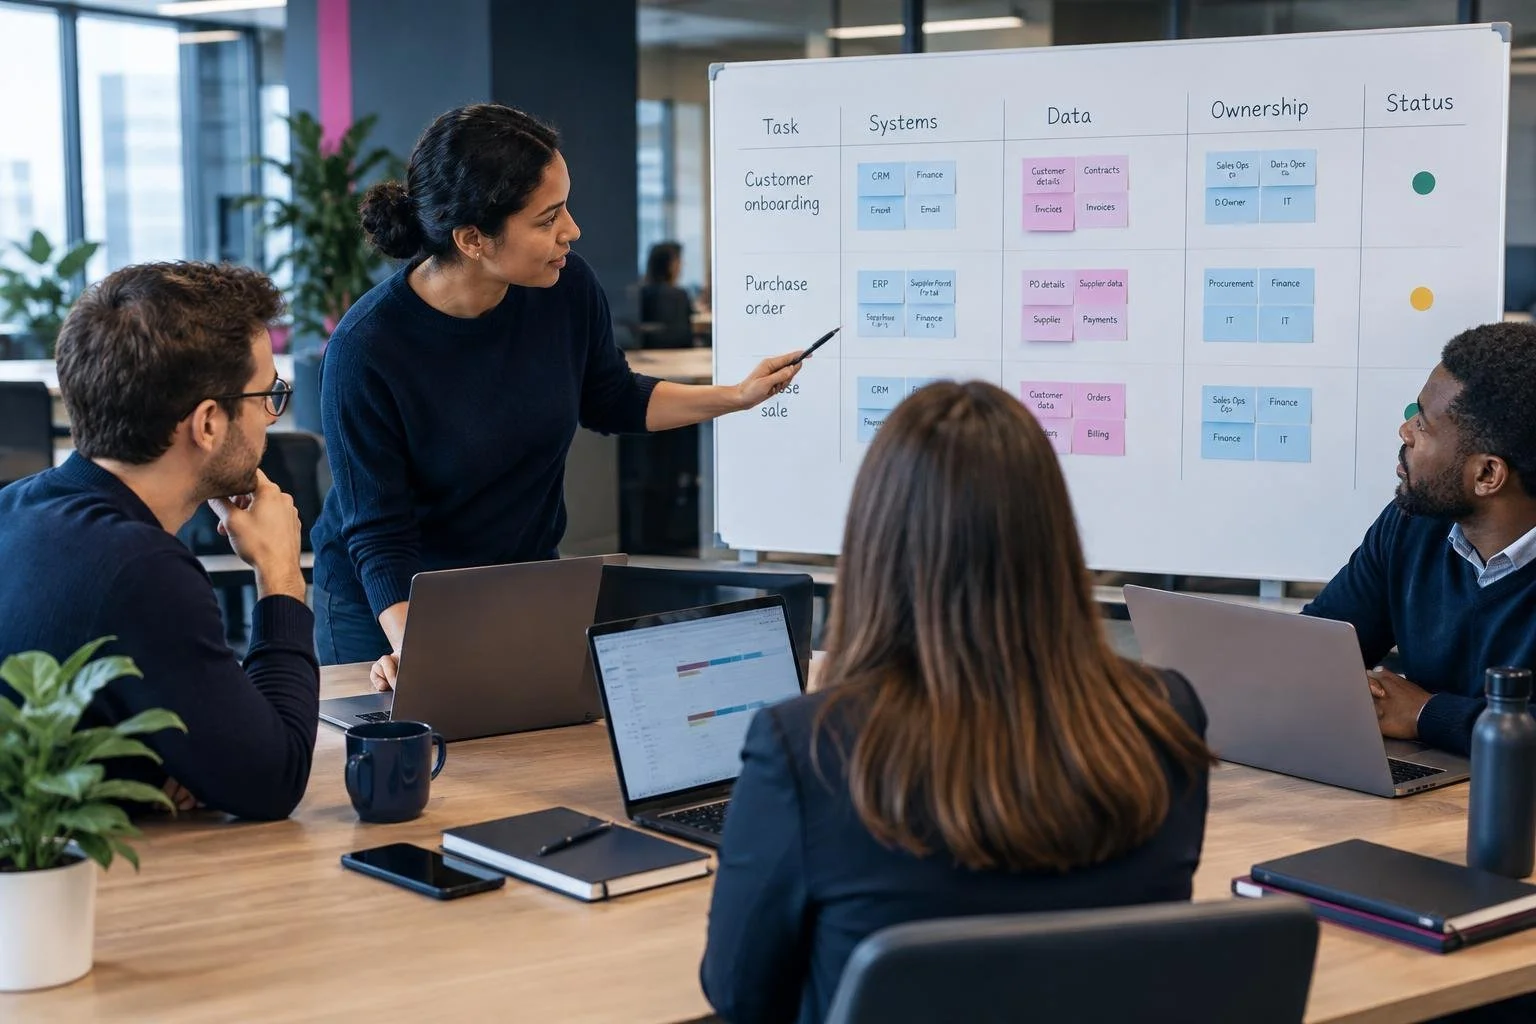
Employees think in tasks, not in application names. To reduce friction, map common end-to-end tasks, such as onboarding a customer, raising a purchase order, or closing a sale. For each task, record every system involved and where data is copied or transformed. This is where manual handoffs and duplicated effort show up clearly.
A simple exercise is to ask the team to walk through a task while you watch, noting every login, copy-paste and approval step. Often the low-hanging improvements are process changes or small automations that remove repeated data entry, rather than replacing whole systems.
Treat integrations and access as first-class assets
Security teams often see attacks originating through forgotten integrations or external suppliers. If an integration exists, treat it like software you own. Document who built it, where the credentials are stored, and what failure looks like.
Likewise, make access reviews routine. Rather than an annual exercise nobody wants to run, build access checks into role changes and leavers processes. Automate parts of this where it makes sense, for example by revoking access automatically when HR records a leaver, while leaving human review for sensitive systems.
Prepare AI and automation by cleaning the foundations
AI can amplify good work, but it will also amplify poor data and unclear responsibilities. Before you give any AI agent broad access, ask where its source data will come from, who owns the accuracy of that data, and which approvals are needed if the agent will act across systems.
Start small. Pilot AI on read-only tasks or narrow, repeatable processes where data quality is already decent. Use those pilots to expose data gaps and ownership blind spots. At the same time, document the decision trails so humans can see why the machine made a recommendation, and who ultimately signs off.
Make visibility continuous, not one-off
A digital footprint is never static. New systems will be added, suppliers will change, teams will reorganise. That means your approach must be ongoing. Two simple habits make a big difference:
Capture updates where people already work. If a team creates a new integration, they should update the short operational summary as part of the deployment checklist. Small changes become manageable when they are embedded into existing workflows.
Schedule lightweight reviews around meaningful events. Treat acquisitions, restructures and major transformation programmes as triggers for a fresh look. These events often reintroduce the same complexity that went unnoticed day to day.
Accept trade-offs, prioritise ruthlessly
You cannot solve everything at once. There are trade-offs between strict central control, which can slow teams down, and loose autonomy, which accelerates innovation but increases risk. The sensible path is to be pragmatic: defend the most critical assets and processes, and allow controlled freedom elsewhere.
Use a risk tiering approach. Protect critical services and datasets with tighter ownership, access reviews and monitoring. For less critical tools, require a minimal operational summary and a sunset plan, so the tool does not become permanent by default.
Practical next steps for business leaders
Ask for a short list of the organisation's most critical services and datasets, and confirm who owns them. Ownership means maintaining a short operational summary.
Run a task mapping workshop for three high-value processes, and identify at least one small automation or process change that will remove repeated manual work.
Treat integrations and third-party connections as assets, and check that credentials and responsibilities are documented.
Pilot any AI or agent-led automation on constrained problems, with clear data ownership and an approval path.
Visibility is not a final project, it is a habit. Start with ownership, map the tasks that matter, and make small, repeatable improvements. Over time those habits reduce risk, improve employee experience, and make automation and AI safe to scale.